Download Fortinet NSE 5 - FortiSwitch 7.6 Administrator.NSE5_FSW_AD-7.6.ExamTopics.2026-10-11.24q.vcex
| Vendor: | Fortinet |
| Exam Code: | NSE5_FSW_AD-7.6 |
| Exam Name: | Fortinet NSE 5 - FortiSwitch 7.6 Administrator |
| Date: | Oct 11, 2026 |
| File Size: | 4 MB |
How to open VCEX files?
Files with VCEX extension can be opened by ProfExam Simulator.
Discount: 20%
Demo Questions
Question 1
Refer to the exhibit.
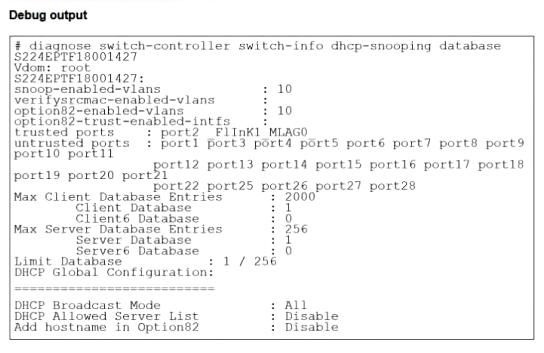
After reviewing the CLI command output, which two conclusions can you make about the Dynamic Host Configuration Protocol (DHCP) snooping configuration? (Choose two.)
- DHCP snooping is disabled globally.
- DHCP broadcasts are not restricted.
- Option 82 is enabled on VLAN 10.
- All ports are untrusted, except port2.
Correct answer: B, C
Question 2
You are designing a multi-tenant network using FortiSwitch devices in standalone mode. Security is a priority and each tenant’s servers must be completely isolated from one another, and from all other servers in the network, to prevent lateral communication. However, all servers must have access to the shared FortiGate firewall for internet access.
Which type of private VLAN (PVLAN) configuration should you apply to meet these security requirements?
- Primary VLAN
- Community VLAN
- Isolated VLAN
- Standalone VLAN
Correct answer: C
Question 3
What happens when a routed VLAN interface (RVI) is configured on a FortiSwitch port or trunk?
- VLAN 1 is automatically assigned for management.
- All VLANs on the port are terminated in a trunk by default.
- The port becomes a layer 3 interface and assigned to VLAN 1.
- The port becomes a layer 3 interface with VLAN 4095 assigned automatically.
Correct answer: D
Question 4
Which statement about 802.1X security profiles using MAC-based authentication mode is true?
- FortiSwitch can implement the use of an access point (AP) for this mode.
- FortiSwitch can grant each device a different access level based on the credentials provided.
- FortiSwitch allows connectivity to all hosts connected to a port, if one host is authenticated.
- FortiSwitch must communicate with the RADIUS server to authenticate devices.
Correct answer: D
Question 5
You enable Dynamic Host Configuration Protocol (DHCP) snooping on a VLAN and configure a FortiSwitch port as trusted for DHCP snooping.
What additional step is required to configure the port as trusted for Dynamic ARP Inspection (DAI)?
- Enable IP Source Guard (IPSG) on the port.
- Manually set the port as trusted for DAI through the CLI.
- DAI implicitly trusts the port.
- Enable static MAC learning on the port.
Correct answer: C
Question 6
Which three are valid actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose three.)
- Assign the VLAN ID
- QoS
- Traffic processing
- Quarantine devices
- Set outer VLAN tags
Correct answer: A, B, E
Question 7
Refer to the exhibit.
Routing Monitor -
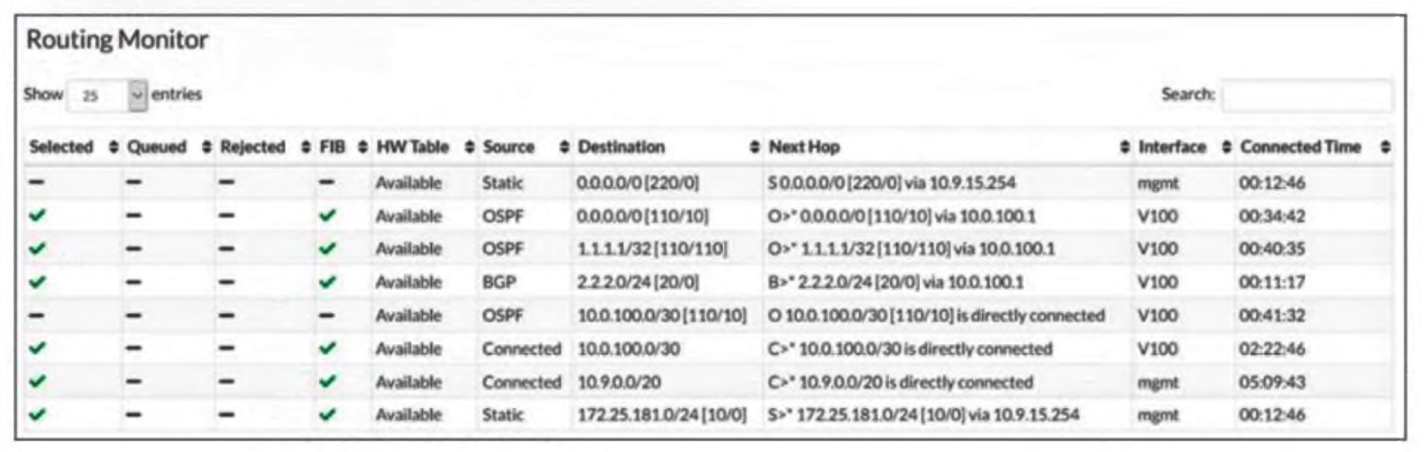
The routing monitor displays multiple route entries, but only some are installed in the forwarding information base (FIB).
After analyzing the two route entries with the destination 0.0.0.0/0, which statement correctly describe why one of these routes is not installed in the FIB?
- The OSPF route has a higher metric, making it less preferred than the static route.
- The interface V100 for the OSPF route is down, preventing its installation.
- The OSPF route with a lower administrative distance is preferred over the static route.
- The two routes have identical destination prefixes, causing a conflict where only one is selected.
Correct answer: C
Question 8
How does FortiSwitch determine the route for traffic traversing its interfaces?
- Hardware-based routing on FortiSwitch is handled by the CPU.
- ASIC hardware routing can handle only dynamic routing, if supported.
- FortiSwitch looks up the hardware routing table and then the forwarding information base (FIB).
- FortiSwitch forwards all traffic to FortiGate for routing decisions.
Correct answer: C
Question 9
Which statement best describes a benefit of using MAC, IP address, or protocol-based VLAN assignments on FortiSwitch?
- It disables 802.1X authentication while preserving user access control.
- It requires devices to authenticate through a RADIUS server before VLAN tagging.
- It assigns ports to VLANs regardless of device type or traffic.
- It offers dynamic segmentation benefits similar to 802.1X authentication.
Correct answer: D
Question 10
Refer to the exhibit.
Debug output -
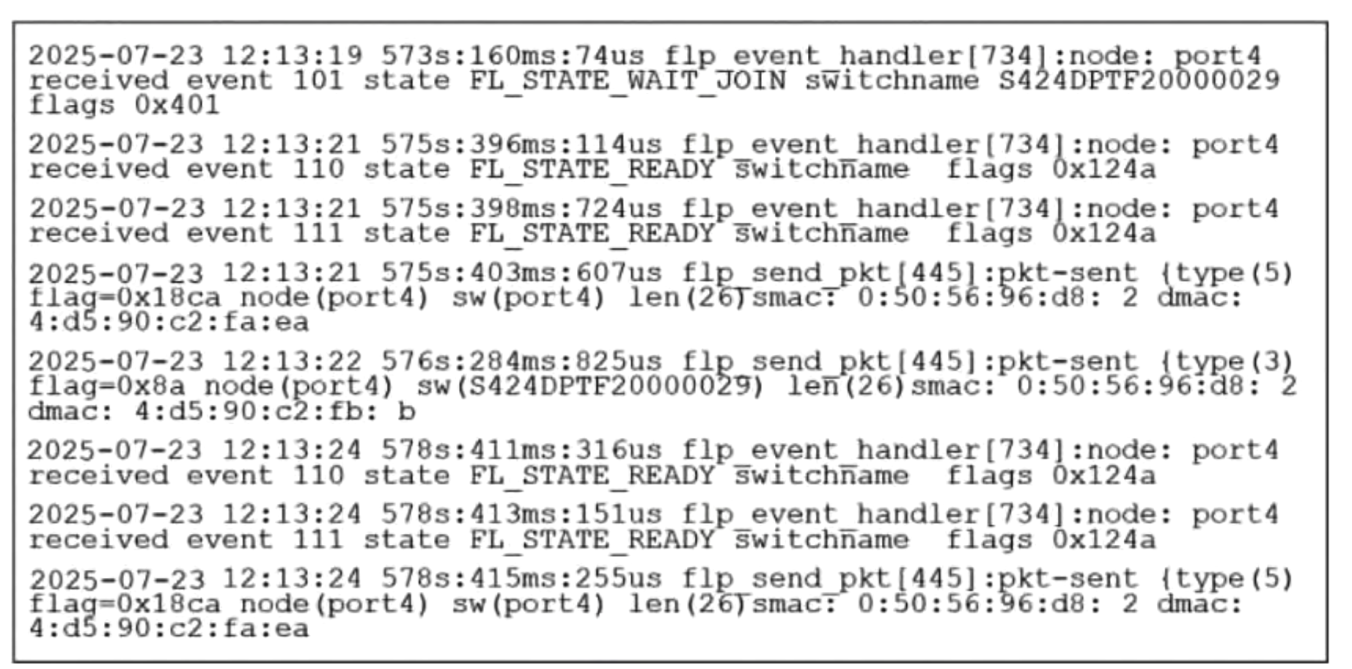
Which two statements best describe what is displayed in the FortiLink debug output shown in the exhibit? (Choose two.)
- FortiSwitch is in a waiting state to join the stack group on FortiGate.
- FortiSwitch is sending FortiLink heartbeats to FortiGate.
- FortiSwitch is discovered and authorized by FortiGate.
- FortiSwitch is sending LLDP-MED inventory management updates to FortiGate.
Correct answer: A, B
HOW TO OPEN VCE FILES
Use VCE Exam Simulator to open VCE files
HOW TO OPEN VCEX AND EXAM FILES
Use ProfExam Simulator to open VCEX and EXAM files
ProfExam at a 20% markdown
You have the opportunity to purchase ProfExam at a 20% reduced price
Get Now!